Brand impersonation → IPO investment fraud | Indian retail investors | Domain suspended within 24 hours
All figures are analyst-captured evidence from the reported campaign.
Executive Summary
In September 2025, a threat actor launched a counterfeit trading portal at crmf-sys[.]com, impersonating Canara Robeco Mutual Fund, one of India’s oldest asset managers. The site cloned the brand’s logotype and color system and promoted a mobile-first trading app featuring Portfolio, News, and IPO modules.
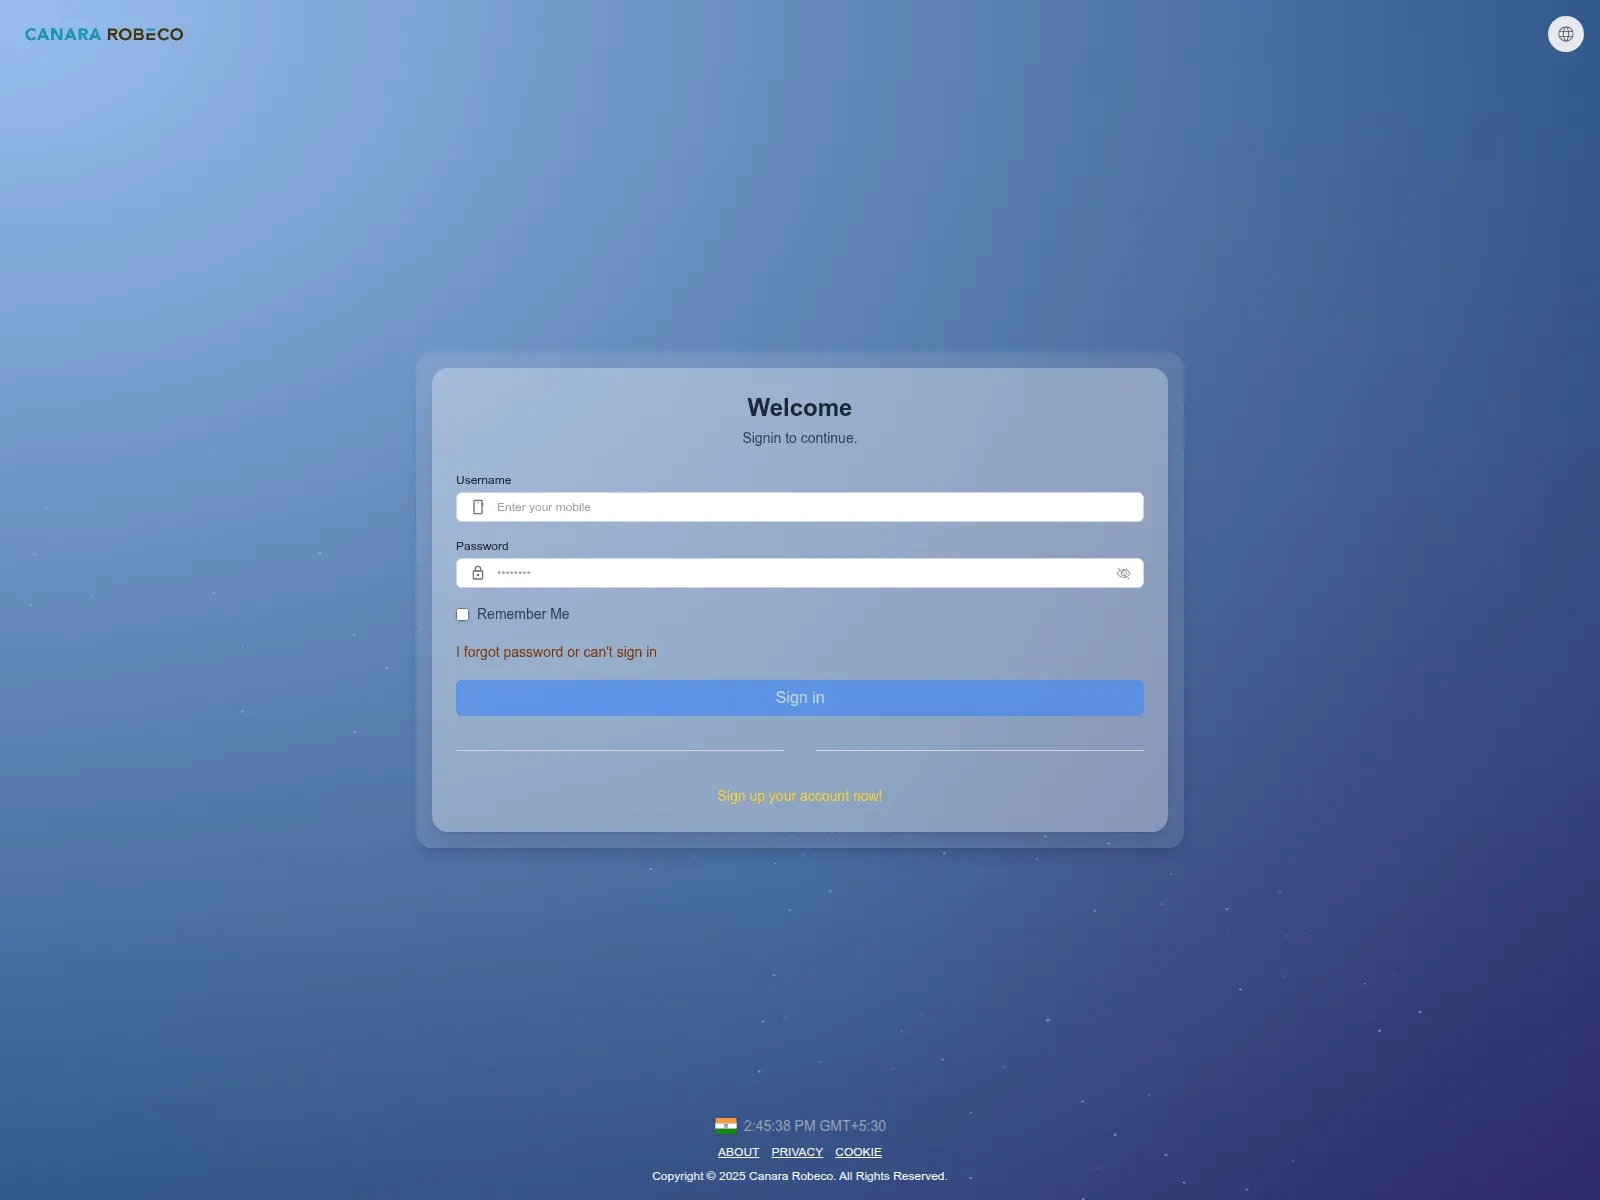
Figure 1 — The crmf-sys[.]com sign-in page. Mobile-number-only authentication, no MFA, cloned Canara Robeco wordmark.
The lure was timed to a real market event: the TechD Cybersecurity Ltd IPO, which opened 15 September 2025 at a ₹183–₹193 band and listed on NSE SME on 22 September. The actor did not invent the IPO — they hijacked it.
Victims were funnelled from WhatsApp and Telegram groups into the portal, where they were offered “institutional allocation” at ₹53 per share against a ₹193 issue price, with projected returns of 420%–600%. Multiple investors filed complaints before the domain was suspended.
The campaign is worth studying because it contains no malware, yet outperforms most commodity phishing. The tradecraft sits in the social layer and the fake back-office, not a payload.
What Is a Fake IPO Allocation Scam?
Fake IPO allocation fraud impersonates a regulated institution to sell a discounted pre-listing allotment that does not exist. The objective is not a password; it is a voluntary bank transfer, sustained across multiple deposits.
The model is adjacent to the fake-trading-platform and ramp-and-dump ecosystems documented across Asia, but runs a far shorter cycle. Where pig-butchering grooms for months, an IPO scam compresses the funnel into the three-to-seven day window between an issue opening and its listing. Urgency comes free, supplied by the market calendar.
Operational Workflow
1. Community seeding. Victims are mass-added to a WhatsApp group — here "Level Up League", 107 members — via invite links pushed through social ads and forwards.
2. Authority construction. A persona operating as "Rajnish Narula" plays the “Professor,” a purported Canara Robeco-affiliated analyst. Co-admins post under a Canara Robeco display name and logo.
3. Social proof manufacturing. Shill accounts answer every broadcast within one to three minutes — "Alright, Professor I will definitely apply." The reply cadence is scripted, not organic.
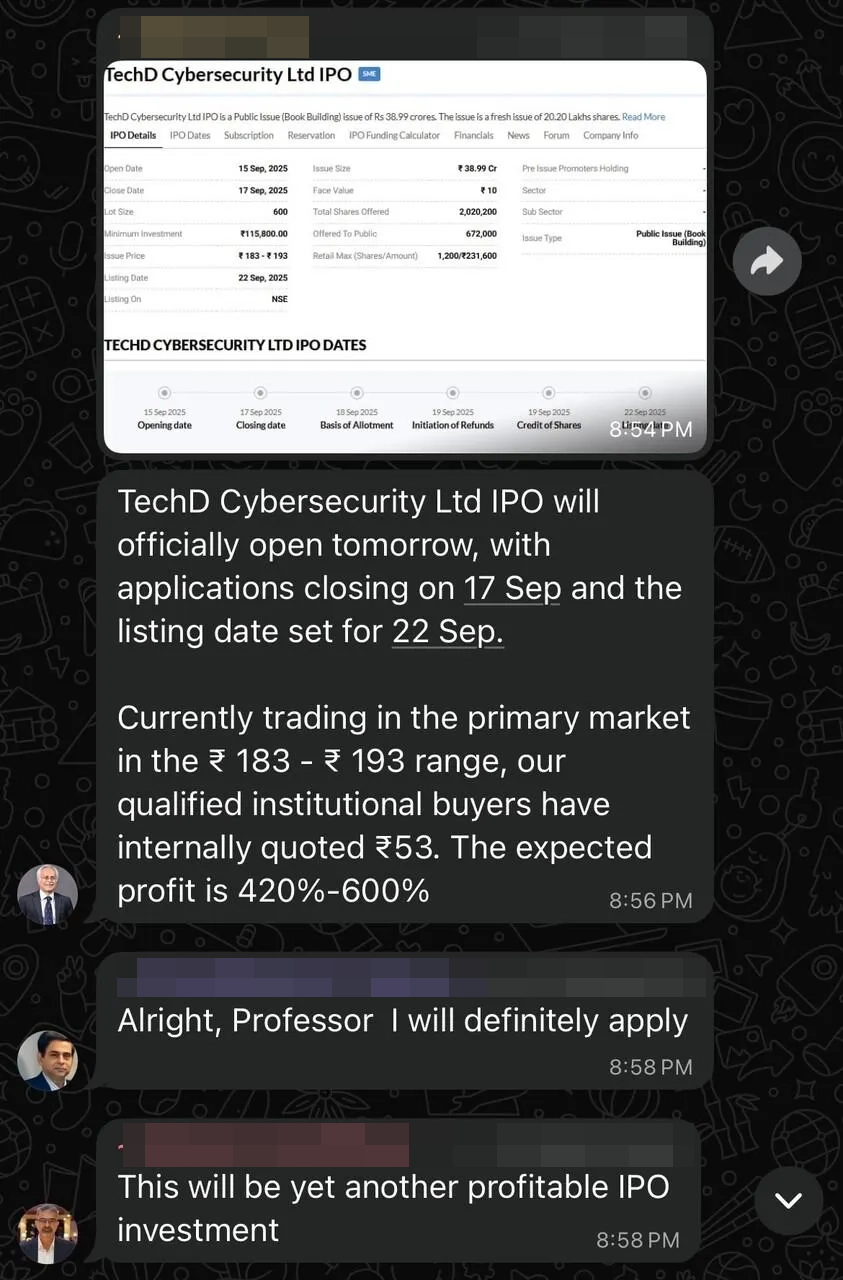
Figure 2 — The "Professor" announces a fabricated Canara Robeco / TechD joint listing. Shill replies land within two to three minutes.
4. Credibility anchoring with true data. The actor posts an authentic IPO fact sheet with correct issue size (₹38.99 Cr), dates and exchange, then inserts one fabricated variable: the "internally quoted" ₹53 allocation. Verifiable truth carries the lie.
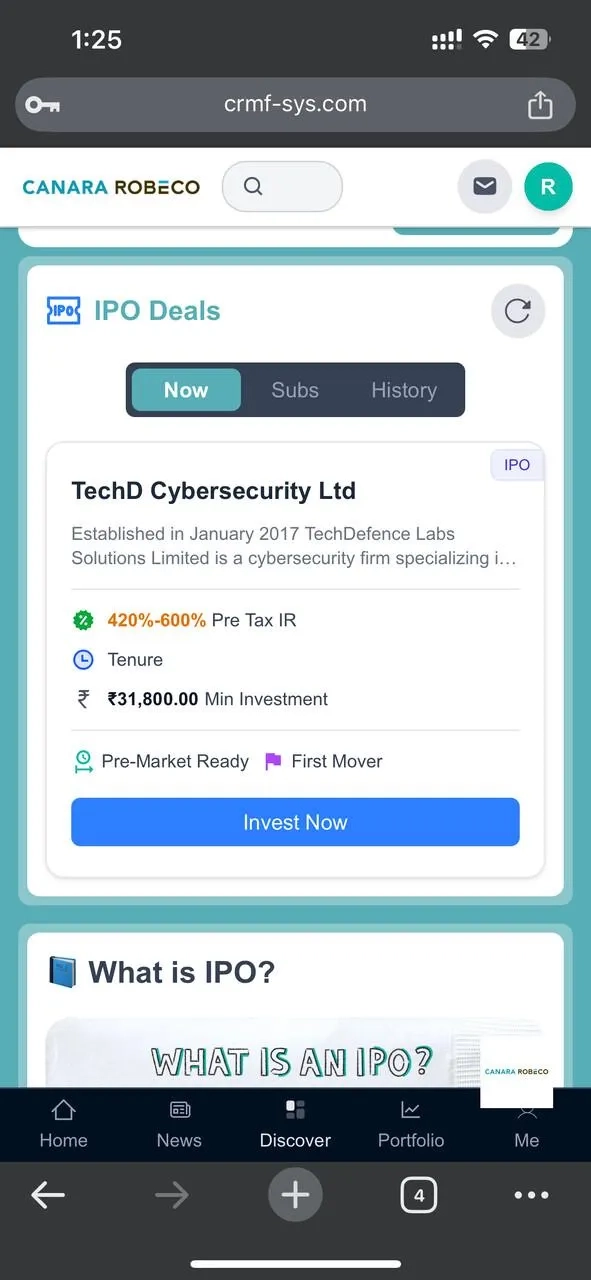
Figure 3 — A genuine IPO fact sheet (correct dates, ₹38.99 Cr issue) paired with the fabricated ₹53 "institutional" quote and a 420%–600% return claim.
5. Platform handoff. Members register at crmf-sys[.]com with a mobile number, open IPO Deals → Now and click Invest Now at a lowered ticket of ₹31,800 against the real ₹1,15,800 lot.
Figure 4 — The conversion surface. Note the reduced ₹31,800 minimum and the "Pre-Market Ready / First Mover" scarcity tags.
Technical Capabilities of the Portal
The platform is a single-page web application, not a native app — a deliberate choice that avoids app store review and sidesteps Android sideloading warnings.
- Mobile-number-only authentication. No email, no MFA. The number doubles as an account key and an enrichment field for follow-up voice pressure.
- A full fake back-office. Home, News, Discover, Portfolio and "Me" tabs render simulated balances, allotment status, and P&L. Victims can watch their money “appreciate.”
- Server-side localisation. A language switcher and a hardcoded GMT+5:30 clock with an Indian flag indicate an i18n-capable kit that can be re-skinned per geography — a reusable framework, not a one-off build.
- Legitimacy furniture. ABOUT / PRIVACY / COOKIE links, an explainer carousel, and a footer reading "Copyright © 2025 Canara Robeco. All Rights Reserved."
The domain string is instructive. crmf compresses Canara Robeco Mutual Fund; -sys mimics an internal system portal. This abbreviation-plus-suffix pattern can evade naive brand-keyword matching that looks only for the full name.
Infrastructure and Persona Analysis
The durable asset here is not the domain. It is the messaging estate.
The admin roster shows a single persona, "Aahana Gill," operating across three numbers — two US VoIP ranges (+1 718, +1 323) and one Indian mobile. Persona identity is decoupled from the phone number, so a ban costs the actor a SIM, not a reputation.
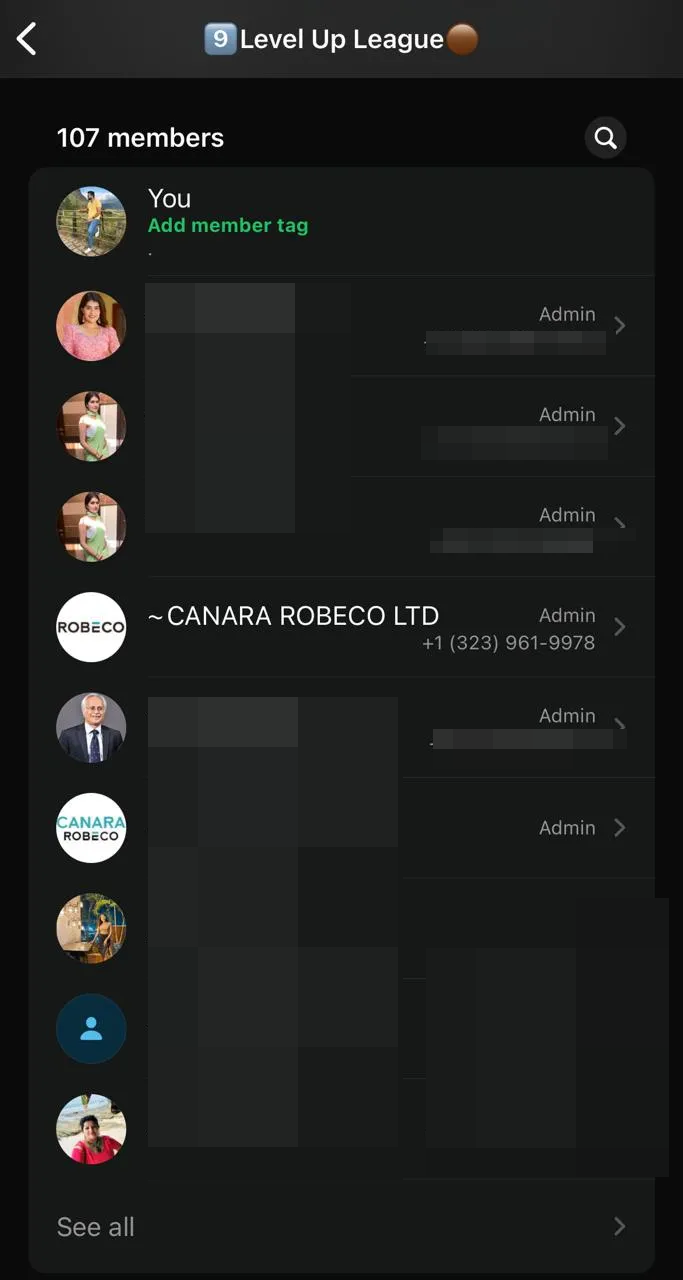
Figure 5 — Seven admins across 107 members. One persona name maps to three numbers, and a Canara Robeco-branded account completes the illusion.
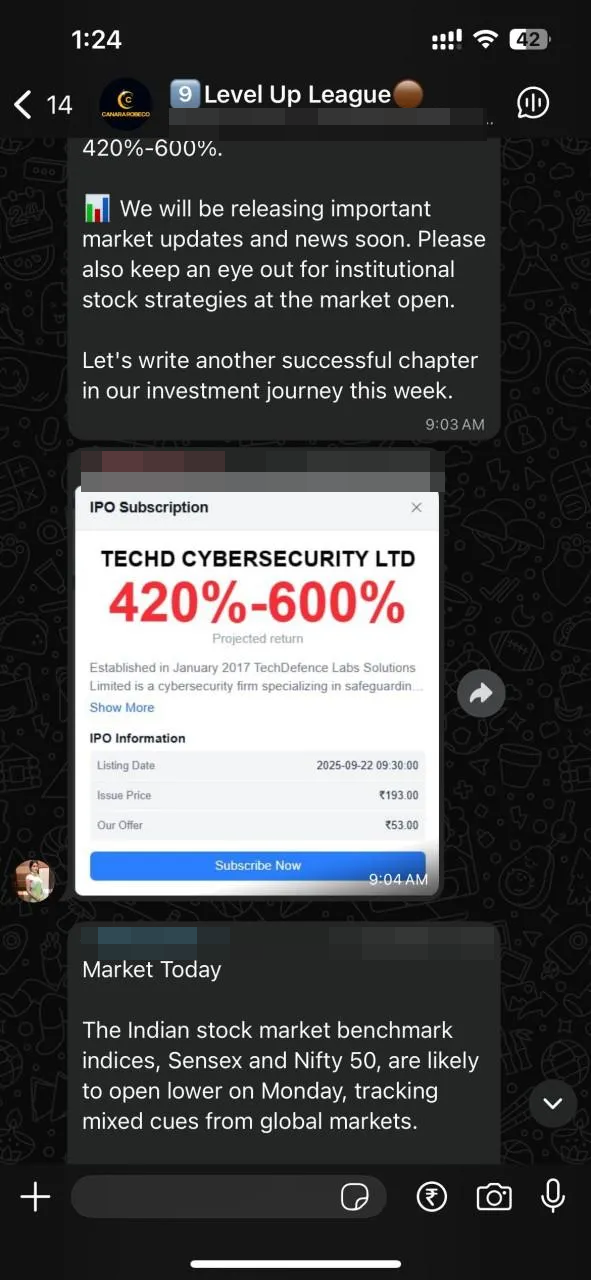
Figure 6 — The in-chat subscription card. A ₹193 issue price alongside a ₹53 “our offer” is the entire economic premise of the fraud.
- Entry deposit at the reduced ₹31,800 minimum—small enough to feel survivable.
- Allocation top-ups, framed as upgrading a “partial allotment.”
- Advance-fee extraction at withdrawal — the portfolio shows a large paper gain, then payout is gated behind “tax,” “clearing,” or “margin verification” fees.
- Victim re-monetisation — verified depositor lists are resold to adjacent crews, often as recovery-scam targets.
Funds land in mule accounts rotated per cohort. Because victims initiate payments through legitimate rails, controls tuned for card fraud or account takeover rarely trigger.
Threat Intelligence Assessment
We assess with high confidence that this is a professionalised, kit-based operation rather than an opportunistic scam, based on the re-skinnable multi-language platform, persona-number decoupling, staffed shill roster and synchronised broadcast cadence.
We assess with moderate confidence that the same infrastructure is reused against other Indian AMC and broker brands, given the generic shell and interchangeable branding layer.
The institutional risk is reputational and regulatory, not technical. No AMC system was breached, yet the brand absorbs complaints, customer losses, and the SEBI and CERT-In reporting burden. Time-to-takedown is the only control that materially reduces harm.
Indicators of Compromise
| Type | Indicator |
|---|---|
| Domain | crmf-sys[.]com |
| Impersonated brand | Canara Robeco Mutual Fund (official: canararobeco.com) |
| Abused security | TechD Cybersecurity Ltd (NSE SME, listed 22 Sep 2025) |
| Group name | "Level Up League" (WhatsApp / Telegram, 107 members) |
| Persona | "Rajnish Narula" / "Rajnish Naru" — the "Professor" |
| Persona | "Aahana Gill" (3 admin numbers) |
| Admin number ranges (defanged) | +1 (323) 961-XXXX ×2, +1 (718) 749-XXXX, +1 (213) 938-XXXX |
| Actor number ranges (defanged) | +91 811XX XXXXX, +91 828XX XXXXX, +91 734XX XXXXX |
| Lure strings | "420%-600% Pre Tax IR", "Pre-Market Ready", "First Mover", "Our Offer ₹53.00" |
| Financial lure | Min investment ₹31,800 vs. genuine ₹1,15,800 lot |
Subscriber numbers are redacted in the published figures and defanged above. Full values are withheld from publication and retained in the evidence package supplied to the registrar and to CERT-In. Numbers rotate per cohort—prioritise the range and pattern over any single value.
Detection and Mitigation
For AMCs, brokers and banks
- Monitor Certificate Transparency logs for abbreviation permutations (
crmf,cr-mf,canararobeco-*) and infrastructure suffixes (sys,portal,invest), not just full brand strings. - Correlate new registrations against your IPO and NFO calendar; spikes in the 14 days before a market event are high-fidelity.
- Pre-authorise registrar, hosting and platform abuse channels so takedown runs in hours, not weeks.
- Treat any “discounted pre-IPO allocation” claim as definitionally fraudulent in customer communications.
For SOC and detection engineering
- Alert on newly registered domains carrying brand tokens in DNS and proxy telemetry; sinkhole via RPZ.
- Hunt the SPA fingerprint: mobile-number-only login,
/ipostyle API routes and hardcoded IST clock components on non-corporate infrastructure.
For incident response and CISOs
- Preserve DNS, WHOIS, hosting and payment-rail records before takedown—suspension destroys evidence prosecution needs.
- Report to CERT-In, SEBI and the National Cybercrime Reporting Portal (cybercrime.gov.in / 1930) inside the golden hour, while reversal is still possible.
- Brief staff directly. Finance team members holding payment authority are the same people joining retail investing groups.
Conclusion
This campaign needed no exploit, no dropper, and no C2. It needed a credible logo, a real IPO, a rented web kit, and a room of scripted personas.
That asymmetry is the point. Defenders are instrumented for compromise, while the highest-volume financial harm now arrives as impersonation — attacks that never touch enterprise infrastructure yet drain the brand’s trust and regulatory standing.
The countermeasure is visibility outside the perimeter: watching the domains, messaging groups and app stores where your brand is being worn by someone else. Here, that visibility bought a same-day takedown. In most cases, it does not exist at all.
About ThreatWatch360
ThreatWatch360 delivers external threat intelligence and brand protection for organisations targeted by impersonation-led fraud, combining domain monitoring, social media monitoring and darkweb monitoring to surface fake portals, rogue apps and counterfeit executive personas before they reach your customers.
Our anti-phishing and anti-rogue operations pair continuous detection with rapid, evidence-preserving takedown across registrars, hosting providers, app stores and messaging platforms. The crmf-sys[.]com domain in this report was identified, evidenced and suspended on the same day it was reported.